Continuous Credential Assurance for Risk Management
We provide continuous, issuer-verified organizational credential status across vendors, suppliers, and subcontractors—strengthening cyber risk, third-party risk, and compliance decisions.
Continuous
Credential Assurance
for Risk Management
We provide continuous, issuer-verified organizational credential status across vendors, suppliers, and subcontractors
strengthening cyber risk, third-party risk, and compliance decisions.
Risk Management Has Changed. Credential Verification Hasn't.
Risk Management Has Changed.
Credential Verification Hasn't.
Organizations continuously monitor cyber risk, third-party risk, and operational conditions. Yet the organizational credentials used to make those decisions are often still verified at a point in time.
Certifications, licenses, and authorizations can expire, be suspended, change scope, or otherwise change between verification cycles.
The documentation already collected may look exactly the same.
The result is a gap between the credential status an organization relies on and the status it can actually verify.
24%
of organizations invest significantly more in proactive cyber measures—including monitoring, assessments, testing, and controls—than reactive measures.
PwC 2026 Global Digital Trust Insights | 3,887 business and technology executives, 72 countries
Credential assurance is part of the same shift: from periodically checking whether something is valid to maintaining visibility as conditions change.
Documentation tells you what was verified.
Continuous assurance tells you whether it is still valid.
Documentation tells you what was verified.
Continuous assurance tells you whether it is still valid.
From Periodic Verification to Continuous Assurance
TRADITIONAL
Credential Verification
VS.
CONTINUOUS
Credential Infrastructure
Collect Documentation
Request certification reports, attestations, and supporting evidence from vendors.
Access & Share Verified Credentials
No need to repeatedly collect or send credential documentation. Credential information is readily available, issuer-verified, and easily shared with authorized organizations.
Validate Credential Claims
Confirm issuer, status, scope, and applicability using available sources.
Monitor Continuously
Issuer-verified status changes become visible between audits and verification cycles.
Track Changes & Expirations
Use AI and automation to flag renewal dates, documentation changes, and potential status issues.
Use Current Status for Risk Decisions
Cyber risk, third-party risk, and compliance decisions are informed by current credential status.
Re-Verify Periodically
Repeat verification during onboarding, renewals, audits, and risk reviews.
Reconcile Across Systems
Update ERP, GRC, vendor management, spreadsheets, and other internal records.
From Periodic Verification to Continuous Assurance
TRADITIONAL
Periodic Verification
-
Collect Documentation
Request certification reports, attestations, and supporting evidence from vendors.
-
Validate Credential Claims
Confirm issuer, status, scope, and applicability using available sources.
-
Track Changes & Expirations
Use AI and automation to flag renewal dates, documentation changes, and potential status issues.
-
Re-Verify Periodically
Repeat verification during onboarding, renewals, audits, and risk reviews.
-
Reconcile Across Systems
Update ERP, GRC, vendor management, spreadsheets, and other internal records.
VS.
CONTINUOUS
Credential Infrastructure
-
Access & Share Verified Credentials
No need to repeatedly collect or send credential documentation. Credential information is readily available, issuer-verified, and easily shared with authorized organizations.
-
Monitor Continuously
Issuer-verified status changes become visible between audits and verification cycles.
-
Use Current Status for Risk Decisions
Cyber risk, third-party risk, and compliance decisions are informed by current credential status.
One Credential. Requested Again and Again.
One Credential.
Requested Again and Again.
Organizations may share the same credential information with dozens of primes each year. Each request can mean finding documentation, confirming what is current, packaging it for another organization, and repeating the process the next time it is requested.
With Validera, the credential record already exists and can be securely shared with authorized organizations without rebuilding the verification package each time.
Verify once at the source. Share when needed. Keep status current.
More Verification Effort Doesn't Create Continuous Assurance
In one enterprise credential environment evaluated by Validera, significant staffing and manual verification processes still couldn't provide continuous visibility into credential status.
The problem wasn't effort. It was the verification model.
30 FTEs supporting credential verification
$2.7M in annual labor cost
$2M+ in uncovered exposure
Still no continuous verification!
30 FTEs supporting credential verification
$2.7M in annual labor cost
$2M+ in uncovered exposure
Still no continuous verification!
Your Existing Systems Aren't the Problem
ERP, GRC, vendor management, and procurement systems manage the information and workflows they were designed to manage. But they typically depend on credential information being entered, uploaded, or periodically refreshed.
Validera adds the missing credential-status layer—providing issuer-verified information that can work alongside the systems organizations already use.
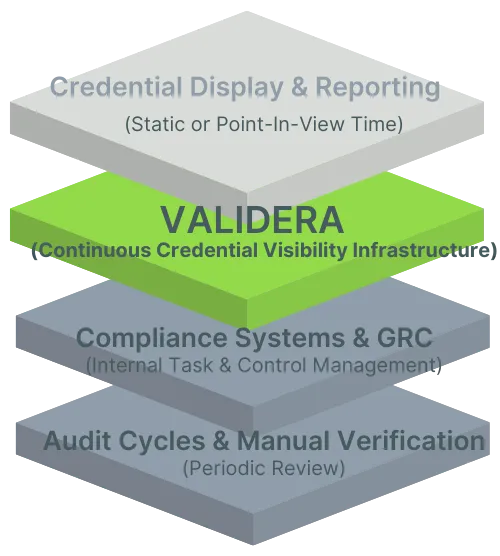
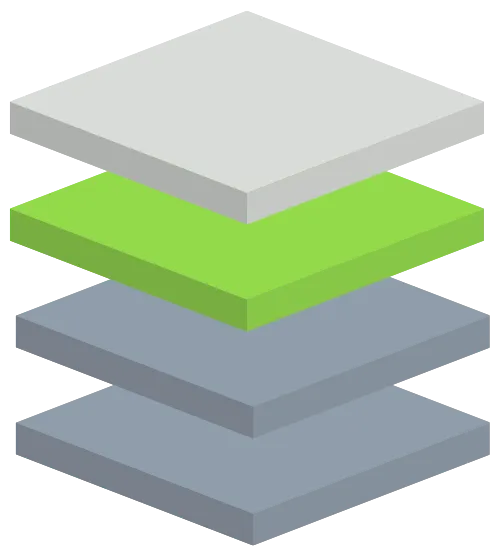
Credential Display & Reporting
Status Visibility & Reporting
VALIDERA — Continuous Credential Assurance
Status Visibility & Reporting
GRC, ERP & Vendor Management
Internal Workflows & Controls
Audits & Periodic Verification
Point-in-Time Verification
Validera doesn't replace the systems you already use. It strengthens them with credential status they weren't designed to continuously verify.
Where Does Credential Reliance Create Risk In Your Organization?
A discovery call isn't a product demo. We'll look at the organizational credentials your business relies on, how they're verified today, where visibility changes between verification cycles, and whether Continuous Credential Assurance fits your environment.
Validera is built for regulated and high-reliance environments, including government contracting, healthcare, energy, and critical infrastructure.
Validera | Patent Pending | ©2026 All Rights Reserved